ISO 27001 Lead Auditor Interview Questions and Answers
Written by Emily Hilton
- What Is ISO 27001, and What Do Its Requirements Cover?
- ISO 27001 Jobs and Lead Auditor Salary
- ISO 27001 Interview Questions and Answers
- Scenario-Based ISO 27001 Questions
- How to Prepare for an ISO 27001 Interview
- Common Mistakes in ISO 27001 Interviews
- Answering Common ISO 27001 Questions
- ISO 27001 Lead Auditor Certification: Where It Fits
- Final Thoughts
ISO 27001 interview questions are where information security hiring gets specific. Employers want candidates who understand the standard itself, not only general cybersecurity, and the interview is often where that gap shows. This guide covers 10 ISO 27001 interview questions and answers, followed by preparation tips and a look at what interviewers expect in ISO 27001 jobs and audit roles.
Demand is easy to explain. ISO Survey data counted 96,709 ISO/IEC 27001 certificates covering 179,877 sites. Every certified organization needs people who can build, run and audit an information security management system (ISMS), and ISO 27001 certification keeps spreading across industries as customers ask for proof of security.
What Is ISO 27001, and What Do Its Requirements Cover?
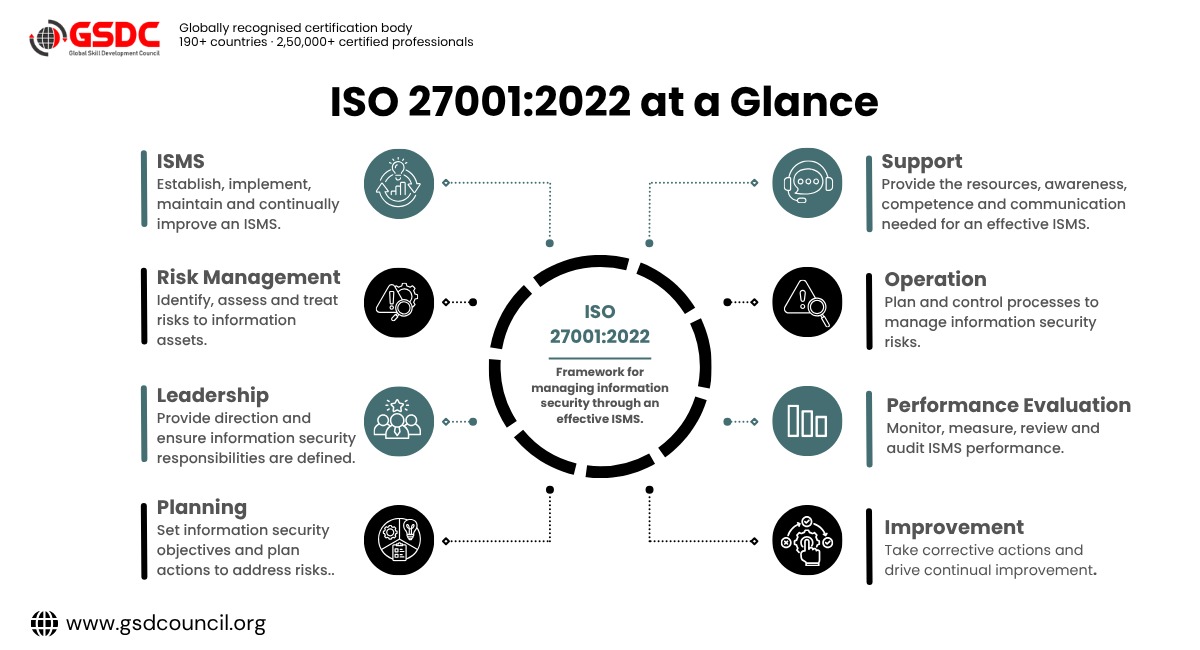
ISO 27001 is the international standard for information security management. The ISO 27001 requirements sit in clauses 4 to 10: context of the organization, leadership, planning, support, operation, performance evaluation and improvement. Annex A adds a catalog of security controls that organizations select based on their risk assessment.
The current edition is ISO/IEC 27001:2022, published in October 2022. The ISO 27001 transition period from the 2013 edition ended on October 31, 2025, and ISO 27001:2013 certificates expire or must be withdrawn after that date. The 2022 update also trimmed the control set from 114 controls in 14 groups to 93 controls in four themes. Interviewers now treat the 2022 edition as the baseline.
ISO 27001 Jobs and Lead Auditor Salary
Roles that ask for ISO 27001 knowledge include ISMS manager, information security analyst, compliance specialist, internal auditor and ISO 27001 lead auditor. Published estimates put the ISO 27001 lead auditor salary in the US at roughly $85,000 to $120,000 a year, though figures vary by source, region and how the role is defined. Strong pay and a recognized standard make interview preparation worthwhile.
ISO 27001 Interview Questions and Answers
1. What is ISO 27001 and why is it important?
ISO 27001 is an internationally recognized standard that provides a framework for establishing, implementing, maintaining and continually improving an ISMS. It matters because it helps organizations identify and manage risks to their information, so valuable data is protected from unauthorized access, disclosure, alteration or destruction.
Certification itself runs on a cycle: an initial audit in two stages, annual surveillance audits and a recertification audit before the three-year certificate expires. Knowing that rhythm helps candidates talk about ISO 27001 certification in practical terms.
2. What are the key requirements and components of an ISMS?
An ISMS is made up of policies, procedures, processes and controls designed to protect an organization's information assets. Key components include risk assessment, risk treatment, security controls, monitoring and continual improvement, all organized under the standard's clauses 4 to 10.
3. How is a risk assessment conducted?
A risk assessment identifies potential risks to an organization's information assets, then evaluates the likelihood and impact of each one and decides which controls will reduce it. A thorough assessment considers internal and external threats, vulnerabilities and business impact.
In practice, the process follows a repeatable order: define the risk methodology and acceptance criteria, identify information assets and their owners, identify threats and vulnerabilities, rate likelihood and impact, prioritize the results in a risk register and then choose a treatment for each risk. Treatment options are to reduce the risk with controls, avoid it, share it (for example through insurance or outsourcing) or accept it with management approval.
4. What is the difference between a risk assessment and a vulnerability assessment?
A risk assessment looks at the full picture: threats, vulnerabilities, likelihood and impact on information assets. A vulnerability assessment is narrower and focuses on finding weaknesses in systems and processes. Vulnerability findings feed into the risk assessment, but they are not the same exercise.
5. What are the different types of security controls?
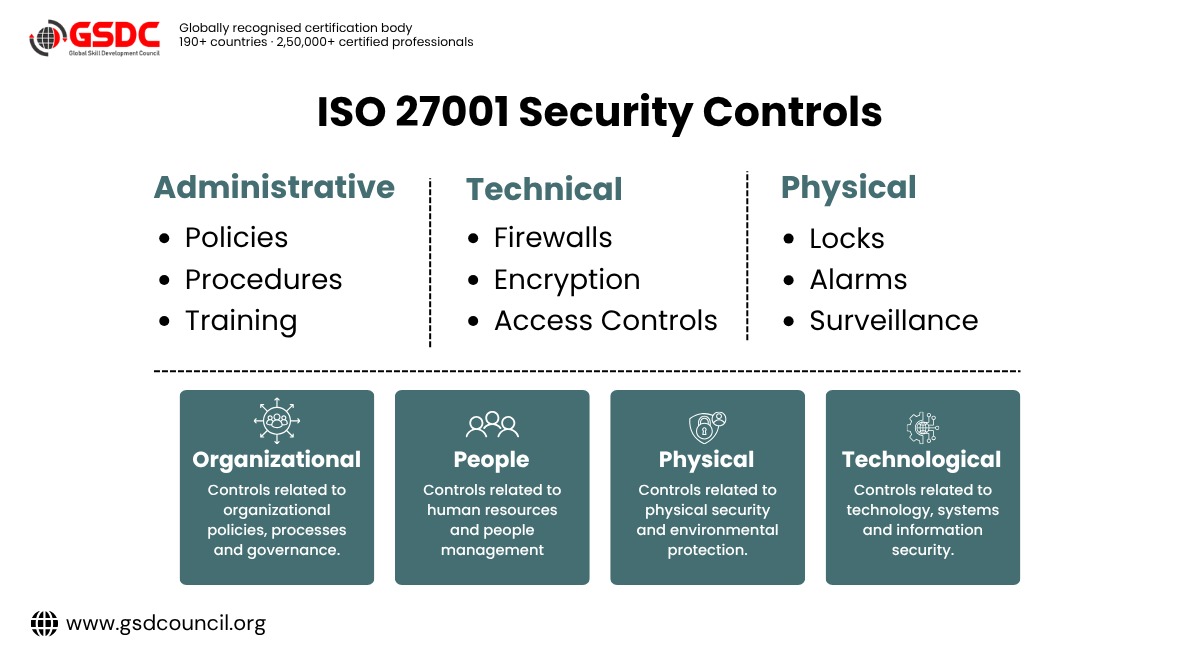
Security controls are commonly grouped as administrative, technical and physical. Administrative controls include policies, procedures and training. Technical controls include firewalls, encryption and access controls. Physical controls include locks, alarms and surveillance systems. Annex A of the 2022 edition organizes its 93 controls into four themes: organizational, people, physical and technological.
6. How is compliance with ISO 27001 ensured?
Compliance requires an ISMS that conforms to the standard's requirements. That means regular internal audits, measuring how effective the ISMS is, taking corrective action when needed and keeping policies aligned with the latest edition of the standard.
7. What is the role of management in an ISMS?
Management sets the information security policy, provides leadership and direction, allocates resources and makes sure the ISMS is built into everyday business processes. Without visible leadership support, an ISMS rarely survives its first audit.
8. How is a security incident handled?
A structured, coordinated approach works best. First identify and contain the incident, then investigate its cause and extent. Once it is under control, reduce the impact, recover, document lessons learned and put measures in place to prevent a repeat.
ISO 27001 expects incident roles, reporting channels and evidence handling to be defined before an incident happens. Good answers mention preserving logs and evidence, communicating with stakeholders and regulators when required, and a post-incident review that feeds corrective actions back into the ISMS.
9. What changed in the transition from ISO 27001:2013 to ISO 27001:2022?
The 2022 edition restructured Annex A into four themes with 93 controls, including 11 new ones such as threat intelligence, data leakage prevention and secure coding. The main clauses were also aligned with other management system standards. The transition period closed on October 31, 2025, so organizations now need certification against the 2022 edition.
A strong answer also covers the practical side: a gap analysis against the updated controls, a revised risk treatment plan and an updated Statement of Applicability, followed by a transition audit with the certification body.
10. What internal audit experience is expected of an ISO 27001 lead auditor?
Internal audits are essential to an effective ISMS. A lead auditor should be able to plan an audit, lead the audit team, gather evidence through interviews, sampling and record review, report nonconformities clearly and follow up on corrective actions. Familiarity with audit techniques and a solid grasp of the standard are expected.
Audit skills are built through practice as much as reading, which is why many candidates turn to structured ISO training. Bodies such as the Global Skill Development Council (GSDC) offer ISO programs for lead auditor roles, and working through audit planning and reporting exercises there gives candidates real material to draw on when this question comes up.
Scenario-Based ISO 27001 Questions
Interviewers often follow the core questions with scenarios. These ISO 27001 questions test judgment more than recall.
What happens when an audit finds a nonconformity?
The nonconformity is documented with evidence and graded as major or minor. The auditee then analyzes the root cause, proposes corrective action and sets deadlines, and the auditor verifies the fix, either in a follow-up or at the next audit. Recurring issues point to a weakness in the ISMS itself, not just a one-off error.
How is the scope of an ISMS defined?
Scope covers the parts of the organization, locations, assets and processes the ISMS protects, along with interfaces and dependencies on third parties. It should reflect business objectives, legal requirements and the expectations of interested parties, and it must be documented. A scope that is too narrow weakens the value of certification, while one that is too broad is hard to manage.
What is a Statement of Applicability, and why does it matter?
The Statement of Applicability lists every Annex A control, states whether it applies, explains why it was included or excluded and records its implementation status. Auditors use it to check that control choices trace back to the risk assessment.
How is the effectiveness of security controls measured?
Through defined metrics and monitoring, such as incident counts and response times, patching rates, access review results and audit findings. Results go to management review, where trends drive improvement decisions.
How to Prepare for an ISO 27001 Interview
Preparation combines technical knowledge, practical examples and clear communication.
1. Study the standard: Read the clauses and Annex A, and understand the key concepts, processes and controls.
2. Review past experience: Pick projects that show real ISO 27001 work and prepare specific examples.
3. Research the organization: Industry, size and security challenges shape what an interviewer cares about.
4. Practice common ISO 27001 questions out loud: It builds clarity and confidence.
5. Highlight relevant credentials: A qualification such as the Certified ISO 27001:2022 Auditor shows commitment to professional development and familiarity with the current edition of the standard, which interviewers tend to value.
6. Show soft skills: Teamwork, communication and problem solving carry real weight in security roles.
7. Prepare questions for the interviewer: It shows genuine interest and helps judge whether the role fits.
Get the latest ISO 27001 Audit Report Template & Checklist featuring:Looking for ISO 27001 Audit Checklist
Common Mistakes in ISO 27001 Interviews
- Reciting clause numbers without a real example of how the requirement was applied.
- Treating risk assessment and risk treatment as the same step.
- Skipping the Statement of Applicability when discussing controls.
- Relying on 2013 terminology and ignoring the 2022 edition.
- Telling vague audit stories with no scope, finding or outcome.
- Overstating credentials or experience, which auditors tend to spot quickly.
Answering Common ISO 27001 Questions
A few habits make answers stronger:
- Be concise and specific: Answer the question asked and back it with a real example.
- Show problem-solving: Explain how a situation would be approached and why.
- Stress attention to detail: Accuracy matters when identifying vulnerabilities and implementing controls.
- Communicate clearly: Complex concepts should make sense to non-technical stakeholders.
- Show adaptability: New threats and changing regulations are routine in this field.
- Know wider best practice: Familiarity with standards beyond ISO 27001 signals a holistic approach.
ISO 27001 Lead Auditor Certification: Where It Fits
Answers land better when they rest on a structured foundation. For candidates considering ISO 27001 lead auditor certification, the Global Skill Development Council (GSDC) offers the Certified ISO 27001:2022 Lead Auditor program, aligned to the current edition of the standard. Whether it is the right step depends on experience and target role, so comparing a few ISO 27001 certification routes against real job listings is a sensible first move.
Final Thoughts
ISO 27001 expertise is a real career accelerator. When an interview comes, thorough preparation is what separates one candidate from the rest, and the questions above are a solid starting point for it.
With data breaches in the headlines, professionals fluent in ISO 27001 find no shortage of options. Use these ISO 27001 interview questions as a springboard to the next information security role.
Related Certifications
Frequently Asked Questions
It is the international standard for building and maintaining an information security management system.
Clauses 4 to 10 cover context, leadership, planning, support, operation, performance evaluation and improvement, and Annex A lists the controls.
No. The transition period ended on October 31, 2025, and organizations now need certification against the 2022 edition.
US estimates run from roughly $85,000 to $120,000 a year, depending on source, region and experience.
Stay up-to-date with the latest news, trends, and resources in GSDC
If you like this read then make sure to check out our previous blogs: Cracking Onboarding Challenges: Fresher Success Unveiled
Not sure which certification to pursue? Our advisors will help you decide!