Certified ISO 27001:2022 Lead Auditor
ISO 27001 Lead Auditor Certification is based on Information Security Management System (ISMS) and Global Compliance Standards
Learn directly from global practitioners, ISO 27001 experts, and industry leaders who are shaping the future of information security
What Sets Our Program Apart?
- Globally Recognized Certification with Self-Paced Learning
- E-Learning Library Access, Ebook
- LinkedIn Enhancer & Professional Resume Builder
- Capstone Projects
- Generative AI Interview Practice Platform
100% Money Back Guarantee on One-Click


About ISO 27001 Certification
Objectives of ISO 27001 Lead Auditor Certification
By completing the ISO 27001:2022 Lead Auditor Certification, you will be able to:
- Understand the principles, requirements, and structure of ISO/IEC 27001:2022 and Information Security Management Systems (ISMS).
- Plan, conduct, manage, and report first-party, second-party, and third-party ISMS audits.
- Evaluate information security risks, security controls, and organizational compliance against ISO 27001 requirements.
- Apply audit principles and techniques to collect evidence, review documentation, and assess control effectiveness.
- Identify nonconformities, recommend corrective actions, and support continual improvement of an ISMS.
- Understand how AI supports information security, including threat detection, risk assessment, and compliance monitoring.
- Evaluate information security practices against applicable legal, regulatory, and industry requirements.
- Develop practical auditing skills through case studies, hands-on exercises, GSDC Studio, and the Learn by Doing approach.
Benefits of ISO 27001 Lead Auditor Certification
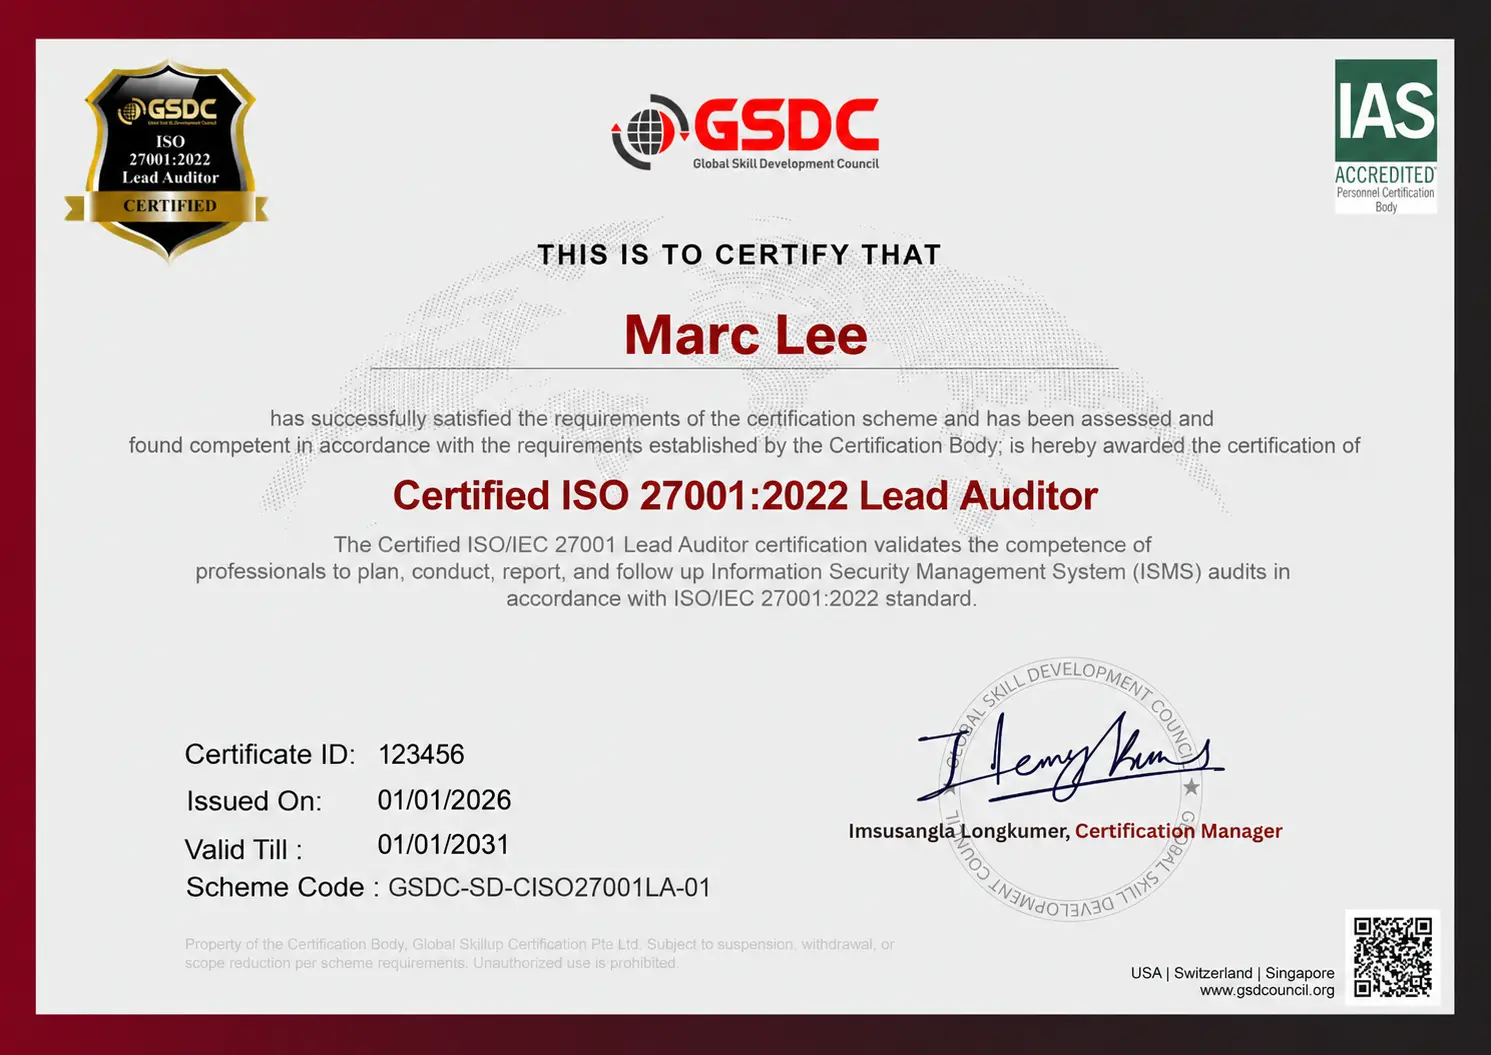
- Earn the Certified ISO 27001:2022 Lead Auditor credential through an IAS-accredited personnel certification framework.
- Build expertise in information security management, ISMS auditing, and ISO 27001 compliance.
- Strengthen your ability to assess security risks, review controls, and report audit findings.
- Learn how AI-assisted techniques can support threat analysis, risk assessment, and security auditing.
- Access GSDC Studio live sessions to learn from experts and explore current industry practices.
- Apply your knowledge through Learn by Doing activities, practical exercises, and real-world audit scenarios.
- Get access to study materials, e-books, toolkits, templates, practice exams, and other learning resources.
- Strengthen your professional profile for opportunities in information security auditing, cybersecurity governance, risk management, and compliance.
Exam Syllabus Of ISO 27001 Lead Auditor Certification
1 ISO 27001:2022 & Information Security Management System+
•Introduction to ISO/IEC 27001:2022
•Information Security Management System (ISMS)
•Purpose and Benefits of ISO 27001
•Information Security, Cybersecurity, and Privacy
•ISO 27001:2022 Structure and Clauses 4–10
•Key Terms and Definitions
•Risk-Based Approach to Information Security
•Confidentiality, Integrity, and Availability (CIA)
•ISMS Scope and Boundaries
•ISO 27001 Certification Process
•Role and Responsibilities of an ISO 27001 Lead Auditor
2 Context of the Organization & ISMS Scope+
•Understanding the Organization and Its Context
•Internal and External Issues
•Interested Parties and Their Requirements
•Legal, Regulatory, and Contractual Requirements
•Information Security Requirements
•Determining the ISMS Scope
•Defining ISMS Boundaries
•Information Security Objectives
•Documenting Organizational Context
•Auditing Clause 4 Requirements
3 Leadership, Information Security Policy & Governance+
•Top Management Commitment
•Information Security Policy
•Roles, Responsibilities, and Authorities
•Information Security Governance
•Management Accountability
•Organizational Roles for Information Security
•Security Awareness and Communication
•Information Security Responsibilities
•Management Commitment and Evidence
•Auditing Leadership Requirements
4 Information Security Risk Assessment & Risk Treatment+
•Information Security Risk Management
•Risk Identification
•Asset Identification
•Threats and Vulnerabilities
•Information Security Risk Assessment
•Risk Analysis and Evaluation
•Risk Treatment Options
•Risk Treatment Plans
•Risk Acceptance
•Risk Monitoring and Review
•Information Security Risk Register
•Auditing Risk Assessment and Risk Treatment
5 Statement of Applicability & Information Security Controls+
•Statement of Applicability (SoA)
•Purpose and Structure of the SoA
•Selecting Applicable Controls
•Justification for Control Inclusion and Exclusion
•ISO 27001:2022 Annex A Controls
•ISO 27002:2022 Guidance
•Organizational Controls
•People Controls
•Physical Controls
•Technological Controls
•Control Implementation Evidence
•Auditing the Statement of Applicability
6 ISO 27001:2022 Annex A Security Controls+
•Information Security Policies
•Asset Management
•Access Control
•Identity and Access Management
•Authentication and Access Rights
•Cryptography
•Physical Security
•Operational Security
•Network Security
•Secure Configuration
•Malware Protection
•Backup and Recovery
•Logging and Monitoring
•Vulnerability Management
•Supplier Security
•Cloud Security
•Incident Management
•Business Continuity and Information Security
•Data Protection and Privacy
•Security Monitoring and Compliance
7 ISMS Implementation, Operations & Security Management+
•Information Security Planning
•Resource Management
•Competence and Awareness
•Information Security Documentation
•Operational Planning and Control
•Change Management
•Information Security Incident Management
•Incident Response
•Business Continuity and Disaster Recovery
•Supplier and Third-Party Security
•Cloud Security Management
•Security Monitoring
•Information Security Performance
•Managing ISMS Changes
8 Performance Evaluation, Internal Audit & Management Review+
•Monitoring, Measurement, Analysis, and Evaluation
•Information Security KPIs and Metrics
•ISMS Effectiveness Evaluation
•Internal Audit Requirements
•Internal Audit Program
•Audit Objectives, Scope, and Criteria
•Audit Planning
•Auditor Competence
•Management Review
•Review Inputs and Outputs
•Evaluating ISMS Performance
•Identifying Improvement Opportunities
9 ISO 19011 Audit Principles & Audit Planning+
•Introduction to ISO 19011
•Principles of Management System Auditing
•Audit Program Management
•Audit Objectives, Scope, and Criteria
•Audit Planning
•Audit Team Selection
•Auditor Competence
•Audit Checklists
•Audit Sampling
•Opening Meetings
•Audit Interviews
•Document Review
•Evidence Collection
•Auditor Independence and Objectivity
10 Conducting ISO 27001:2022 Audits+
•Conducting the Audit
•Audit Trails
•Gathering Objective Evidence
•Document and Record Review
•Interviews and Observation
•Sampling Techniques
•Testing Security Controls
•Verifying Control Effectiveness
•Evaluating ISMS Compliance
•Identifying Gaps and Weaknesses
•Assessing Information Security Risks
•Evaluating Annex A Controls
•Evaluating Statement of Applicability
•Maintaining Audit Evidence
11 Nonconformity, Corrective Action & Audit Reporting+
•Identifying Nonconformities
•Major and Minor Nonconformities
•Audit Findings
•Writing Clear Audit Findings
•Evidence-Based Findings
•Root Cause Analysis
•Corrective Action
•Corrective Action Plans
•Corrective Action Verification
•Audit Conclusions
•Audit Reports
•Closing Meetings
•Follow-Up Audits
•Continual Improvement of the ISMS
12 AI for ISO 27001 Auditing+
•Introduction to AI for ISO 27001 Auditing
•AI-Assisted Audit Planning and Checklists
•AI for ISMS Document and Evidence Review
•AI-Assisted Risk and Control Analysis
•AI for Audit Findings and Report Drafting
•AI Prompts for ISO 27001 Lead Auditors
•Responsible AI, Data Privacy, and Human Auditor Oversight
What Comes with a GSDC Certification?
You will receive a globally recognized GSDC Certified ISO 27001:2022 Lead Auditor credential that validates your ability to audit and evaluate an Information Security Management System. The credential demonstrates your knowledge of ISO/IEC 27001 requirements, risk assessment, Statement of Applicability, Annex A controls, ISO 19011 auditing, evidence collection, nonconformities, corrective actions, and audit reporting.
Learn from Experts
Learn from experienced practitioners and industry leaders who bring real-world expertise and practical insights to the program.

Federico Smith
EXPLEO GROUP
GLOBAL PROGRAM MANAGER
Kathrin Kind
WORLD ECONOMIC FORUM
MEMBER, GLOBAL FUTURE COUNCIL ON DATA FRONTIERS
Ljubomir Trajkovski
TRAJKOVSKI & PARTNERS CONSULTING
PARTNERS MANAGEMENT CONSULTING

Christophe Mazzola
DSCVR CYBERSECURITY
FOUNDER & CEO
Adrian Resag
OCEG
ACADEMIC DIRECTOR
Luv Johar
CYBERGRC SERVICES AND ACADEMY
GLOBAL CYBERSECURITY INFLUENCER | CO-FOUNDER

Nuno Teodoro
HUAWEI
CYBER SECURITY AND PRIVACY OFFICER | CISO
Nelson Al Assal Filho
DBMC CONSULTORIA
GLOBAL EXPERT
Stephen Platten
INSPIRED TESTING
PRINCIPAL CONSULTANT
Krishni Arumugam
HIGH HAZARD INDUSTRIES
PRINCIPAL RISK MANAGEMENT, HSE AND PROCESS SAFETY MANAGE CONSULTANT
Tamara Mackroy, PhD
COMPLIANCE & RISK MANAGEMENT EXPERT ISO | QUALITY | GOVERNANCE | HUMAN SERVICES SYSTEMS| L&D PROFESSIONAL
Kelroy James
DEFENCE INNOVATION CHAMPIONS NETWORK, ROYAL NAVY
STRATEGIC INNOVATION CHAMPION
GSDC Studio
100+ Live Monthly Sessions with Global Experts
Get practical ISO learning in daily 45-minute expert-led sessions. Apply concepts immediately as you work through documentation tasks, internal audit steps, risk assessments, and gap analyses. Build job-ready ISO implementation and auditing capability with support from global consultants and lead auditors.
Session Highlights
4 Daily Sessions
45-minute live expert-led sessions for hands-on learning.
Sessions from Global Experts
Learn directly from leaders around the world.
Real-time Practice
Apply concepts immediately and get your questions answered.
Certification Ready
Training aligned with industry standards for job-ready skills.
Learn by Doing
Don't just watch - Apply what you learn immediately.
How it Works:
Step 1
Watch the Video: Learn each tool through expert-led tutorials.
Step 2
Complete the Guided Challenge: Practice on the same platform and apply your knowledge step by step.
Lifetime Access: Revisit videos and challenges anytime.
Enrollment Options
Single Access
Gain full access to our complete resource library and earn a globally recognized certification.
1 Certificate Programs
Bundle Access
Unlock exclusive bundle savings on premium resources and earn globally recognized credentials.
3 Certificate Programs
For Teams
Enable teams with GSDC certification pathways and customized learning journeys aligned with business priorities.

7 Day Money-Back Guarantee

Target Audience Of Certified ISO 27001 Lead Auditor
Pre-Requisites Of ISO 27001 Lead Auditor
There are no mandatory prerequisites for ISO 27001:2022 but below are a few recommendations: Recommended to have training on ISO 27001:2022 through a qualified training institution. Recommended to have work experience in quality and security.
Exam Details of ISO 27001 Lead Auditor Certificate
Exam Questions
58
Exam Format
Multiple choice
Language
English
Passing Score
70%
Duration
120 min
Proctored
Yes
Certification Validity
5 Years
Complimentary Retake
Yes
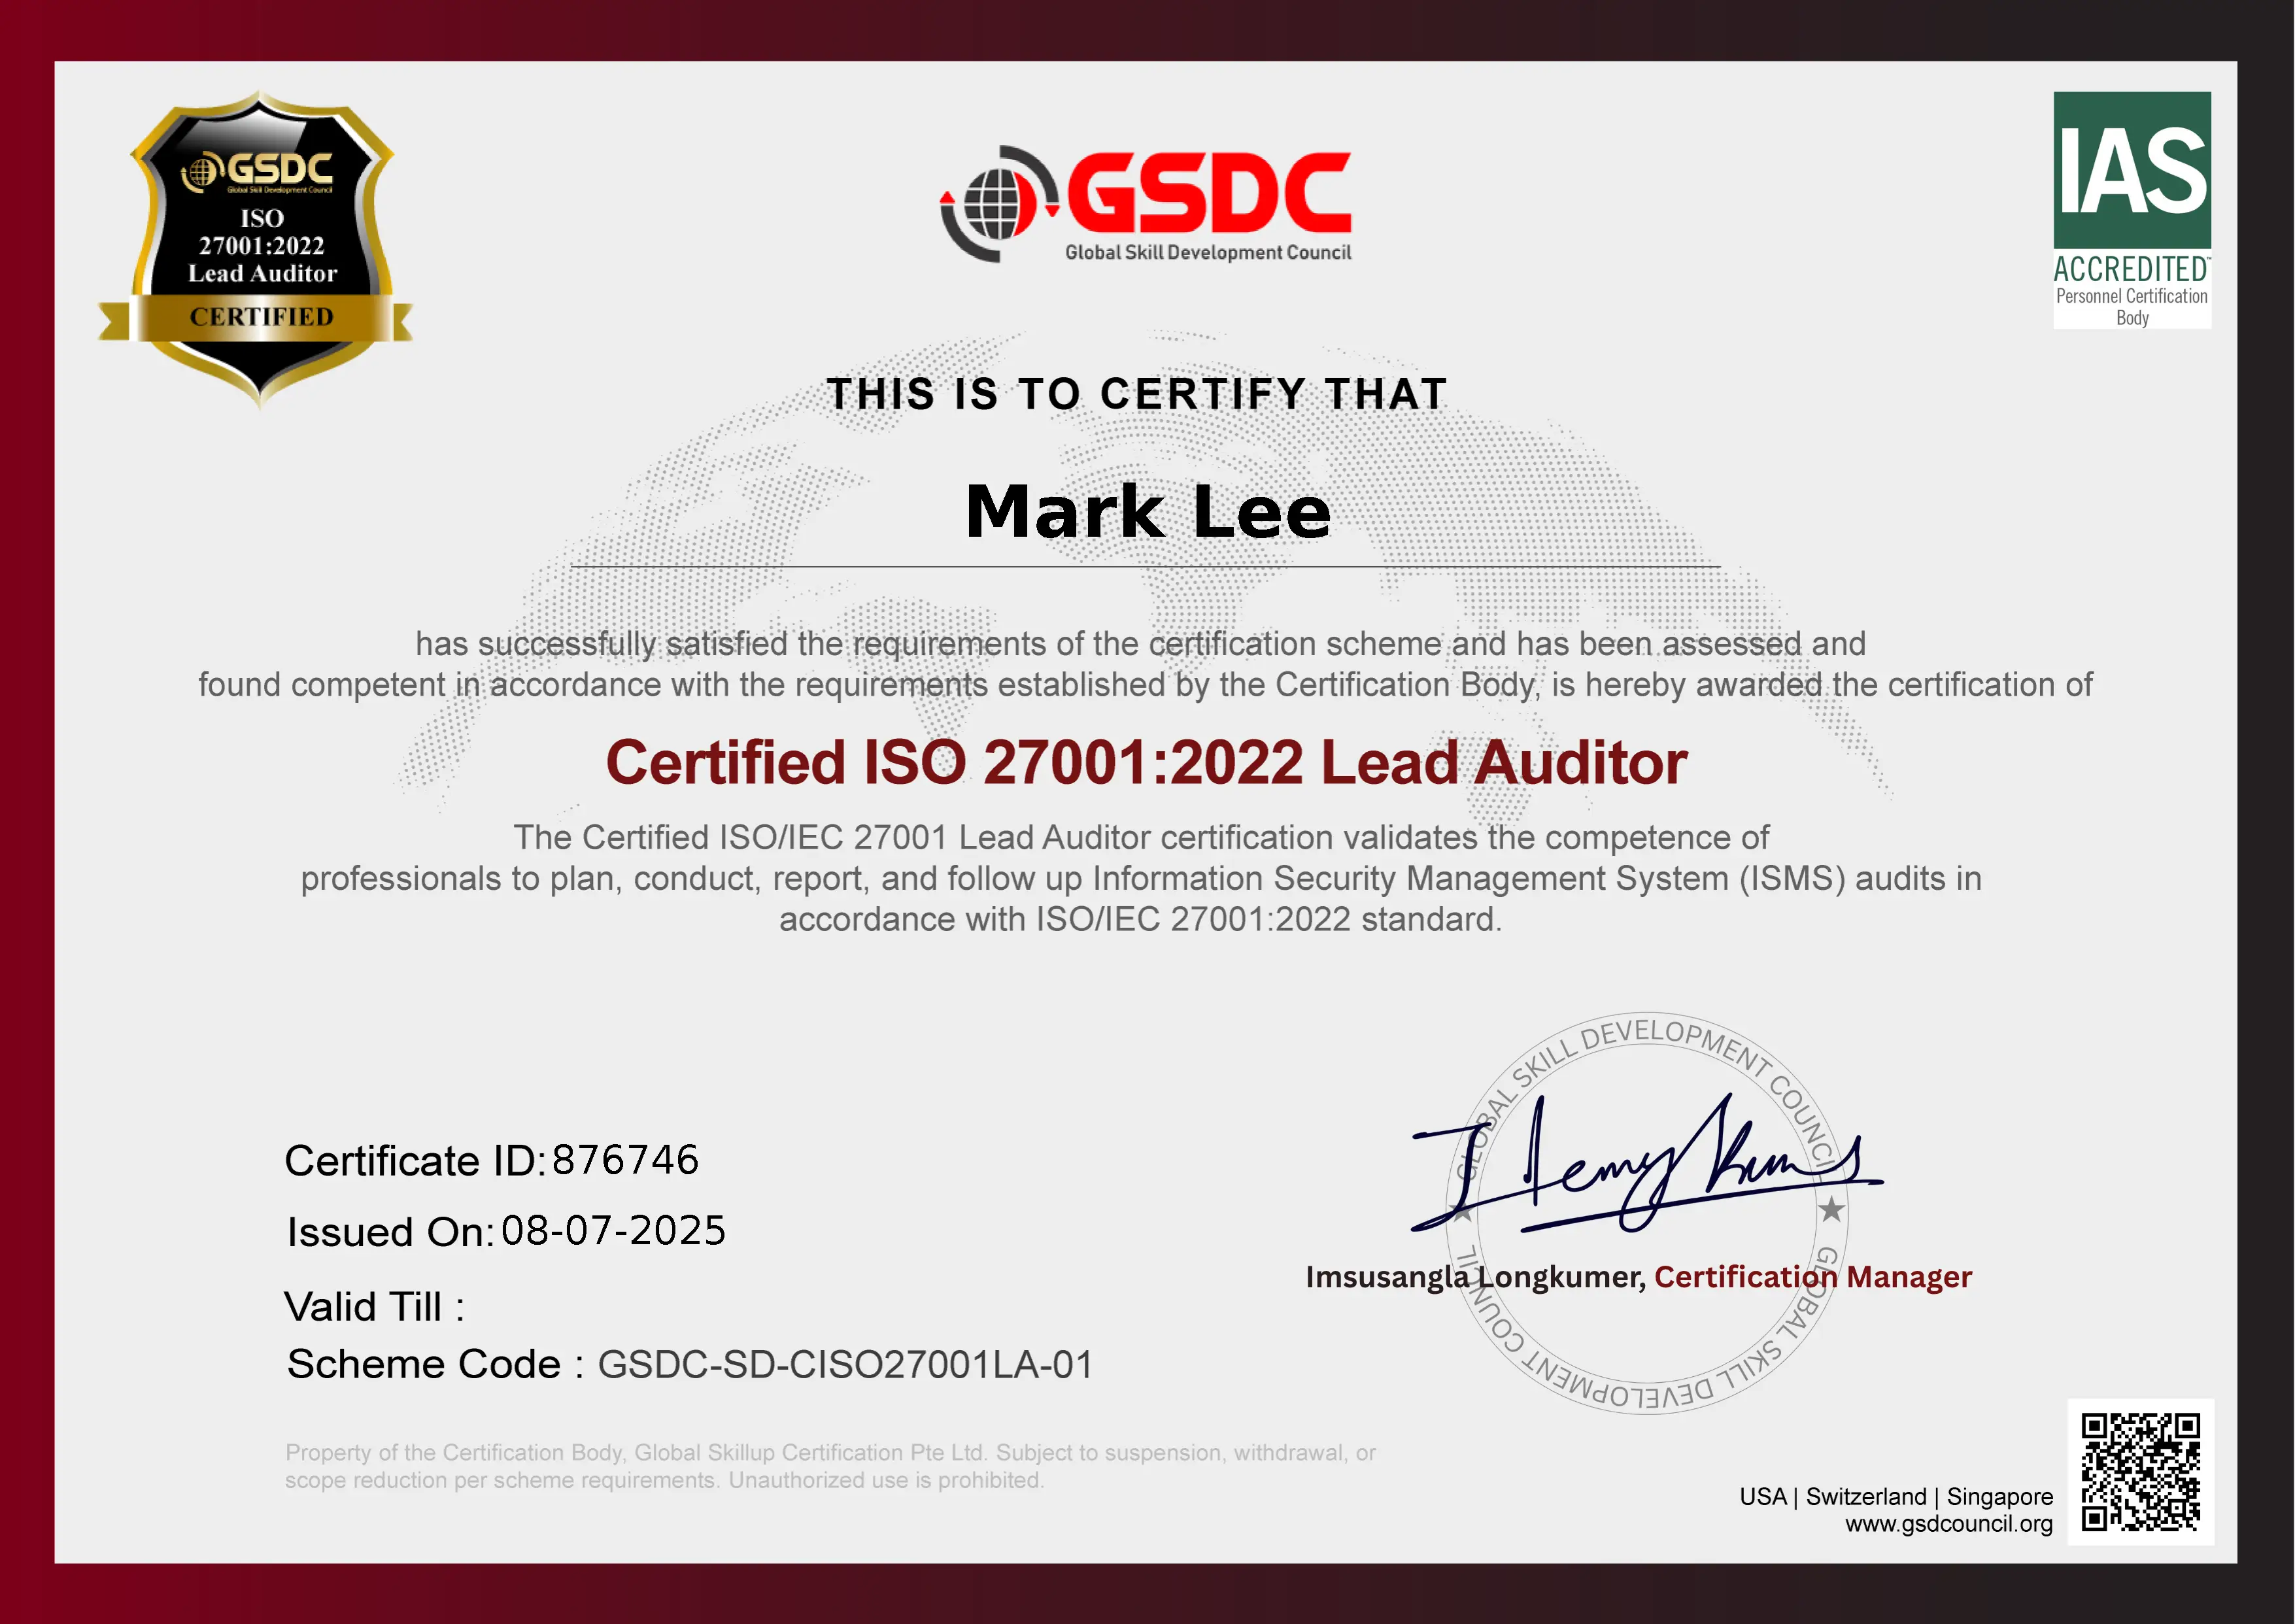
Sample Certification
About ISO 27001 Lead Auditor Certification
The GSDC ISO 27001:2022 Lead Auditor certification equips professionals with the knowledge and practical skills to plan, conduct, manage, and report Information Security Management System (ISMS) audits in accordance with ISO/IEC 27001:2022. The certification covers ISO 27001 clauses, Annex A controls, risk assessment, audit planning, evidence collection, nonconformity management, corrective actions, and audit reporting. It also introduces AI applications in information security, including AI-assisted risk assessment, threat analysis, and compliance monitoring
The ISO 27001:2022 Lead Auditor certification is one of the GSDC certifications accredited by the International Accreditation Service (IAS). GSDC is accredited by IAS as a Personnel Certification Body, PCB-168, with its certification processes aligned with ISO/IEC 17024, the international standard for organizations that certify persons.
With this certification, you get access to self-paced learning resources, GSDC Studio live sessions, Learn by Doing activities, practice materials, and practical auditing resources. You can build your understanding through real-world audit scenarios, hands-on exercises, and expert guidance. The certification is suitable for information security professionals, internal and external auditors, cybersecurity consultants, risk and compliance managers, and governance leaders seeking to strengthen their ISMS auditing skills.


